Skip to content
Facebook X Instagram
Tracy NAR

Tracy NAR

  • Home
  • Blog
  • About
  • Contact
Tracy NAR
Tracy NAR

Risk Management

Home / Risk Management
formula to write a risk statement with condition event consequence
Cybersecurity-risk-assessment | grc-career

How to Write a Strong Cybersecurity Risk Statement (10 Examples)

ByTracy A. October 17, 2026October 6, 2026

The risk register lands in the steering committee meeting at Clearwater Financial Services, and the first entry reads: Cyber attack risk…
Read More How to Write a Strong Cybersecurity Risk Statement (10 Examples)Continue

six steps to conduct a cybersecurity risk assessment
grc-career | IT Careers & Professional Development

How to Conduct a Cybersecurity Risk Assessment: The Practical Step-by-Step Guide

ByTracy A. October 3, 2026October 6, 2026

How to Conduct a Cybersecurity Risk Assessment: Step-by-Step The email lands on a Wednesday. Clearwater Financial Services is renewing its cyber…
Read More How to Conduct a Cybersecurity Risk Assessment: The Practical Step-by-Step GuideContinue

Vulnerability assessment vs penetration testing comparison illustration
IT Audit & Compliance

Vulnerability Assessment vs Penetration Testing: Which Security Test Does Your Organization Need in 2025?

ByTracy A. October 18, 2025October 19, 2025

If you’re trying to figure out the difference between vulnerability assessment vs penetration testing, you’re not alone. Most business leaders struggle…
Read More Vulnerability Assessment vs Penetration Testing: Which Security Test Does Your Organization Need in 2025?Continue

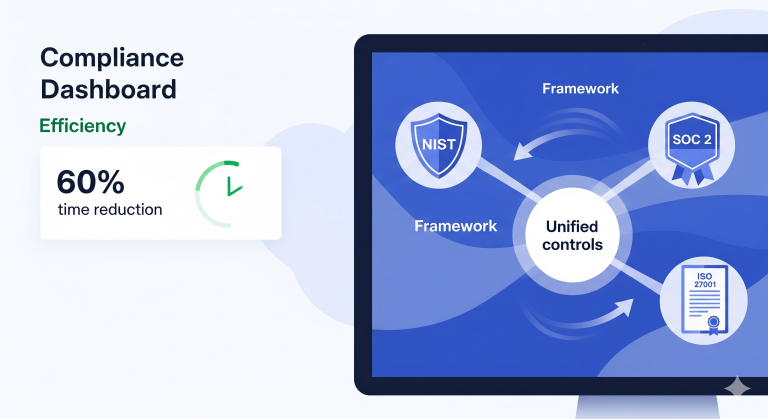
Mapping controls dashboard with NIST SOC 2 ISO 27001 frameworks unified showing 60% time reduction
IT Careers & Professional Development

Mapping Controls: Streamline Multi-Framework Compliance and Reduce Audit Time

ByTracy A. September 9, 2025September 1, 2025

IT auditors spend more time hunting through spreadsheets than analyzing actual risks. The average compliance team recreates the same access control…
Read More Mapping Controls: Streamline Multi-Framework Compliance and Reduce Audit TimeContinue

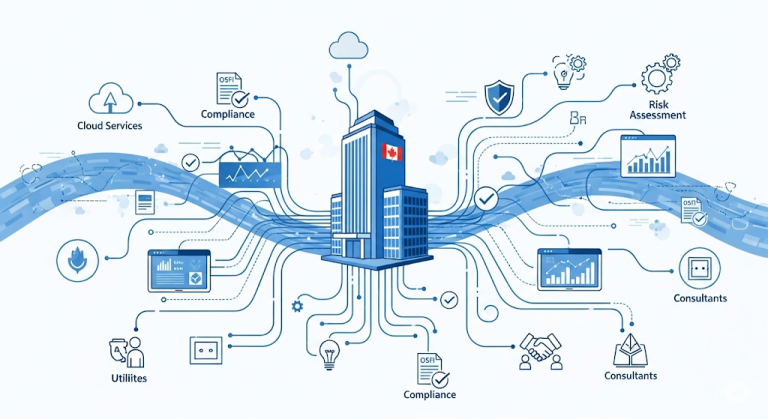
OSFI B-10 third party risk management framework illustration showing Canadian FRFI connected to multiple third-party providers with risk assessment and compliance monitoring elements
Regulatory-deep-dives

OSFI B-10 Third Party Risk Management: Requirements and Framework for Canadian FRFIs (2025)

ByTracy A. July 19, 2025July 25, 2025

Since OSFI’s new B-10 Guideline took effect May 1, 2024, Canadian federally regulated financial institutions (FRFIs) have invested an average of…
Read More OSFI B-10 Third Party Risk Management: Requirements and Framework for Canadian FRFIs (2025)Continue

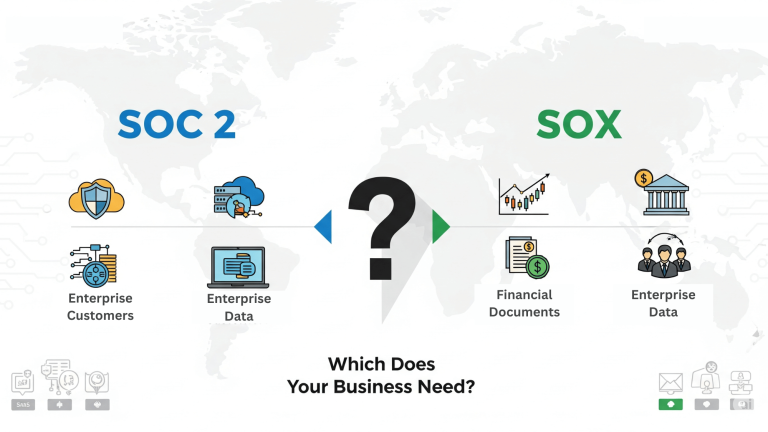
Professional infographic comparing SOC 2 vs SOX compliance frameworks with icons showing SOC 2 for service providers and cloud companies on the left, SOX for public companies and financial reporting on the right, with a central question mark asking which framework businesses need.
Regulatory-deep-dives

SOC 2 vs SOX Compliance: The Essential Decision Framework Your Business Can’t Afford to Miss

ByTracy A. July 7, 2025July 9, 2025

Nearly 70% of service organizations reported the necessity to demonstrate compliance or conformity to at least six different frameworks covering information…
Read More SOC 2 vs SOX Compliance: The Essential Decision Framework Your Business Can’t Afford to MissContinue

Professional business desk with laptop showing security compliance dashboard and ISO 27001 certificate, representing successful certification achievement.
Regulatory-deep-dives

ISO 27001 Certification: Complete 2025 Guide to Process, Costs & Timeline (Step-by-Step)

ByTracy A. June 20, 2025October 8, 2026

According to the official ISO Survey 2023 results showing 48,671 valid ISO 27001 certificates worldwide, organizations typically invest $25,000 to $250,000…
Read More ISO 27001 Certification: Complete 2025 Guide to Process, Costs & Timeline (Step-by-Step)Continue

Canadian GRC compliance illustration showing office building with governance, risk and compliance icons representing federal and provincial regulatory frameworks
Regulatory-deep-dives

GRC Compliance in Canada: PIPEDA, Law 25 & OSFI Guide

ByTracy A. June 6, 2025October 13, 2026

Canadian organizations face complex regulatory environments with compliance costs reaching $51.5 billion annually across all businesses in 2024, according to the…

Read More GRC Compliance in Canada: PIPEDA, Law 25 & OSFI GuideContinue

Tracy NAR
  • Home
  • Blog
  • About
  • Contact

© 2026 Tracy NAR

  • Home
  • Blog
  • About
  • Contact